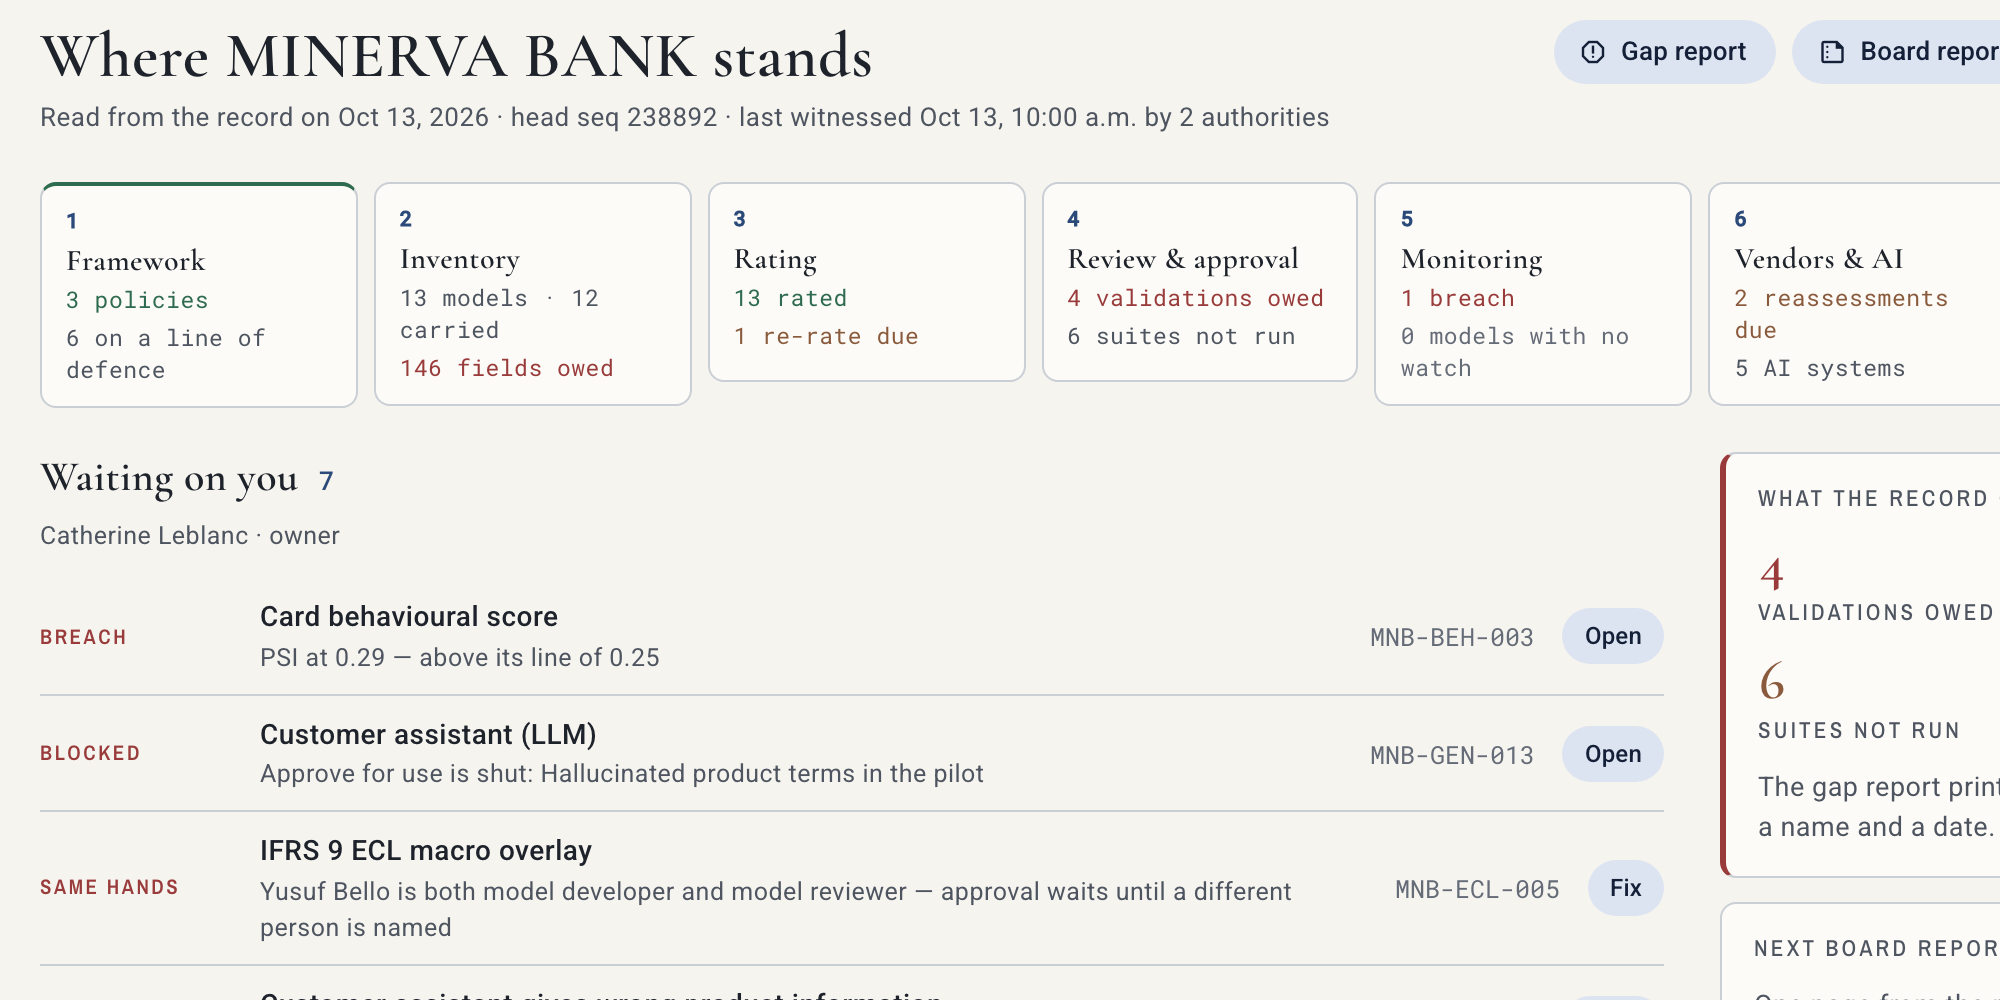
Programme Dashboard
Your E‑23 programme in seven steps, with live counts from the record and your open actions listed first.
Model and AI governance infrastructure for OSFI FRFI
days left
Can you prove that your models and AI are governed?
01 · System of recordsEvery model, owner, policy, vendor and decision sits on one record, with each change hash-chained to the one before.
02 · InventoryEvery model is held in E‑23's own fields: owner, developer, reviewer, approver, risk rating and next review date.
03 · Policy as codeThe guideline's requirements are written as a rule pack, and the record is checked against them on every change.
04 · AssessmentEach model is risk-rated on E‑23's factors by a named person, and the rating sets its validation, monitoring and approval requirements.
05 · ValidationTests run in your own environment on a plan set by the risk rating, and every result is recorded against the model.
06 · System of actionsNo model is approved with a segregation-of-duties conflict, missing evidence or an open high-severity finding, and only a named person approves.
07 · Evidence packetOne package holds every record, time-stamp receipt and signed checkpoint, and your examiner verifies it offline with a single command.
08 · Audit portal / trailEvery change is attributed and time-stamped by independent authorities, and examiners get time-limited, read-only access.
09 · Enterprise supportRun it hosted in Canada, on a dedicated instance or on your own servers, with single sign-on and an open API to the same record.
10 · Rule packsRule packs for OSFI E‑23, SR 26‑2, PRA SS1/23, the NIST AI RMF and the EU AI Act set the fields and approval rules the record must meet.
Frontier modelsCopilotsAgents
Threat detectionZero trustIdentity
Prompt defenceAccess controlGuardrails
Vendors
Model testingIndependent reviewMonitoring
Vendors
Control monitoringAccess reviewsAttestation
Vendors
AccuracyAccountabilityControl
MINERVA
Model inventoryEvidence packetsAudit readiness
forNIST AI RMFOSFI E‑23SR 26‑2
MINERVA provides
Compliance servicesGRC platform
To make you E‑23 compliant
One goal: Govern, Map, Measure and Manage.
Your E‑23 programme in seven steps, with live counts from the record and your open actions listed first.
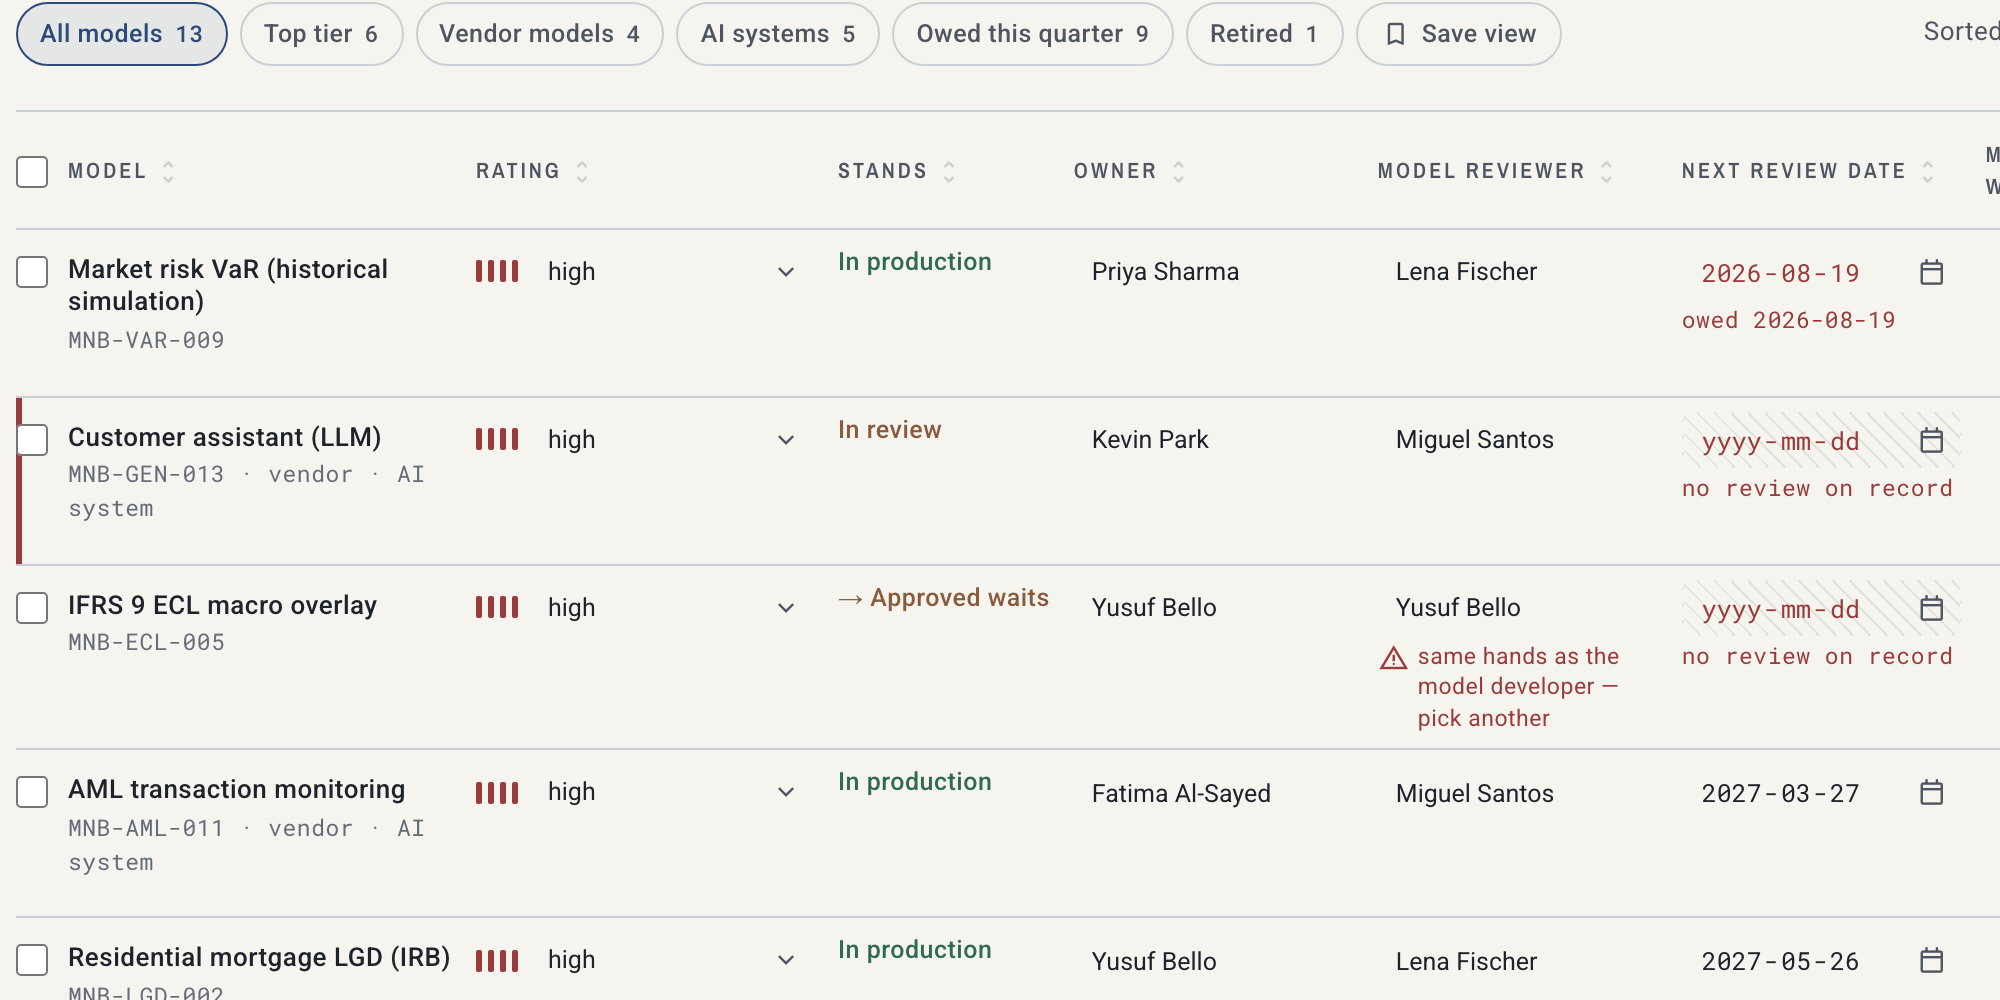
Every model with its owner, risk rating, reviewer, approver, next review date and monitoring status in E‑23's own fields.
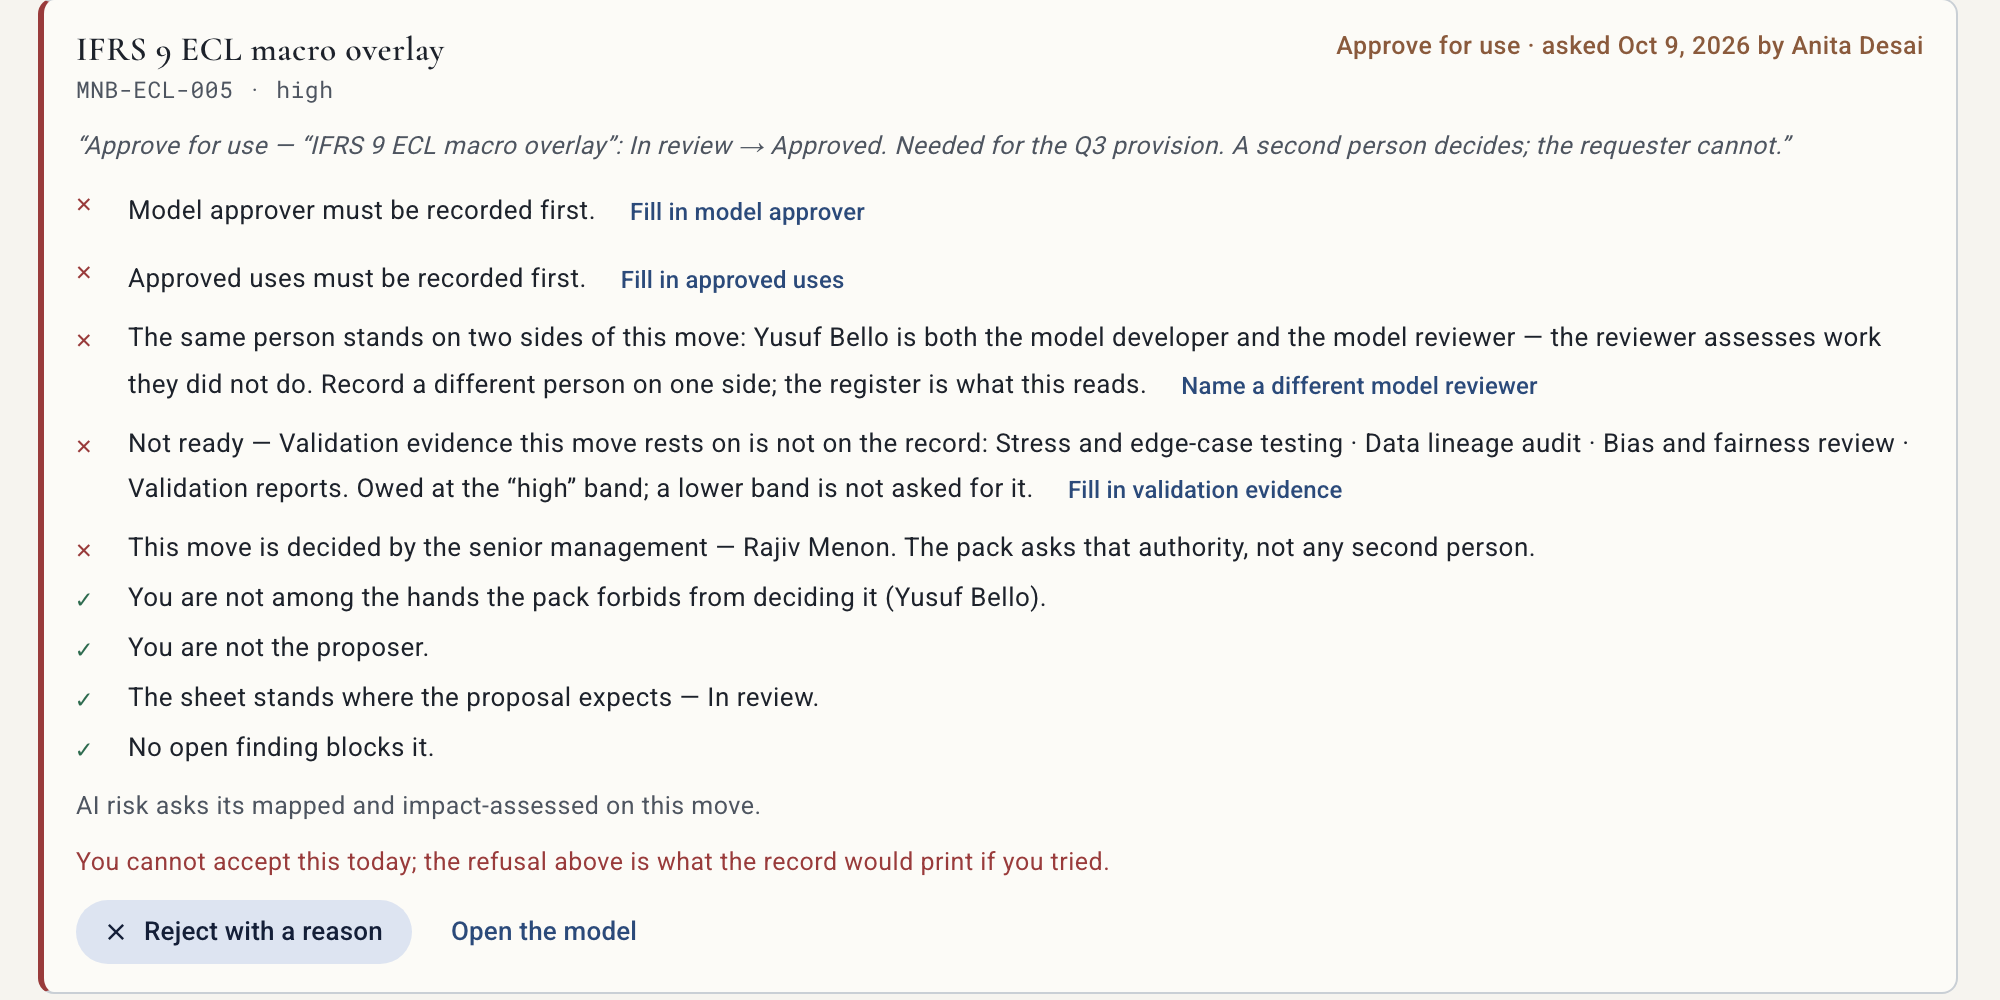
Approval stays blocked until every condition is met, and the card lists each blocker with what resolves it.
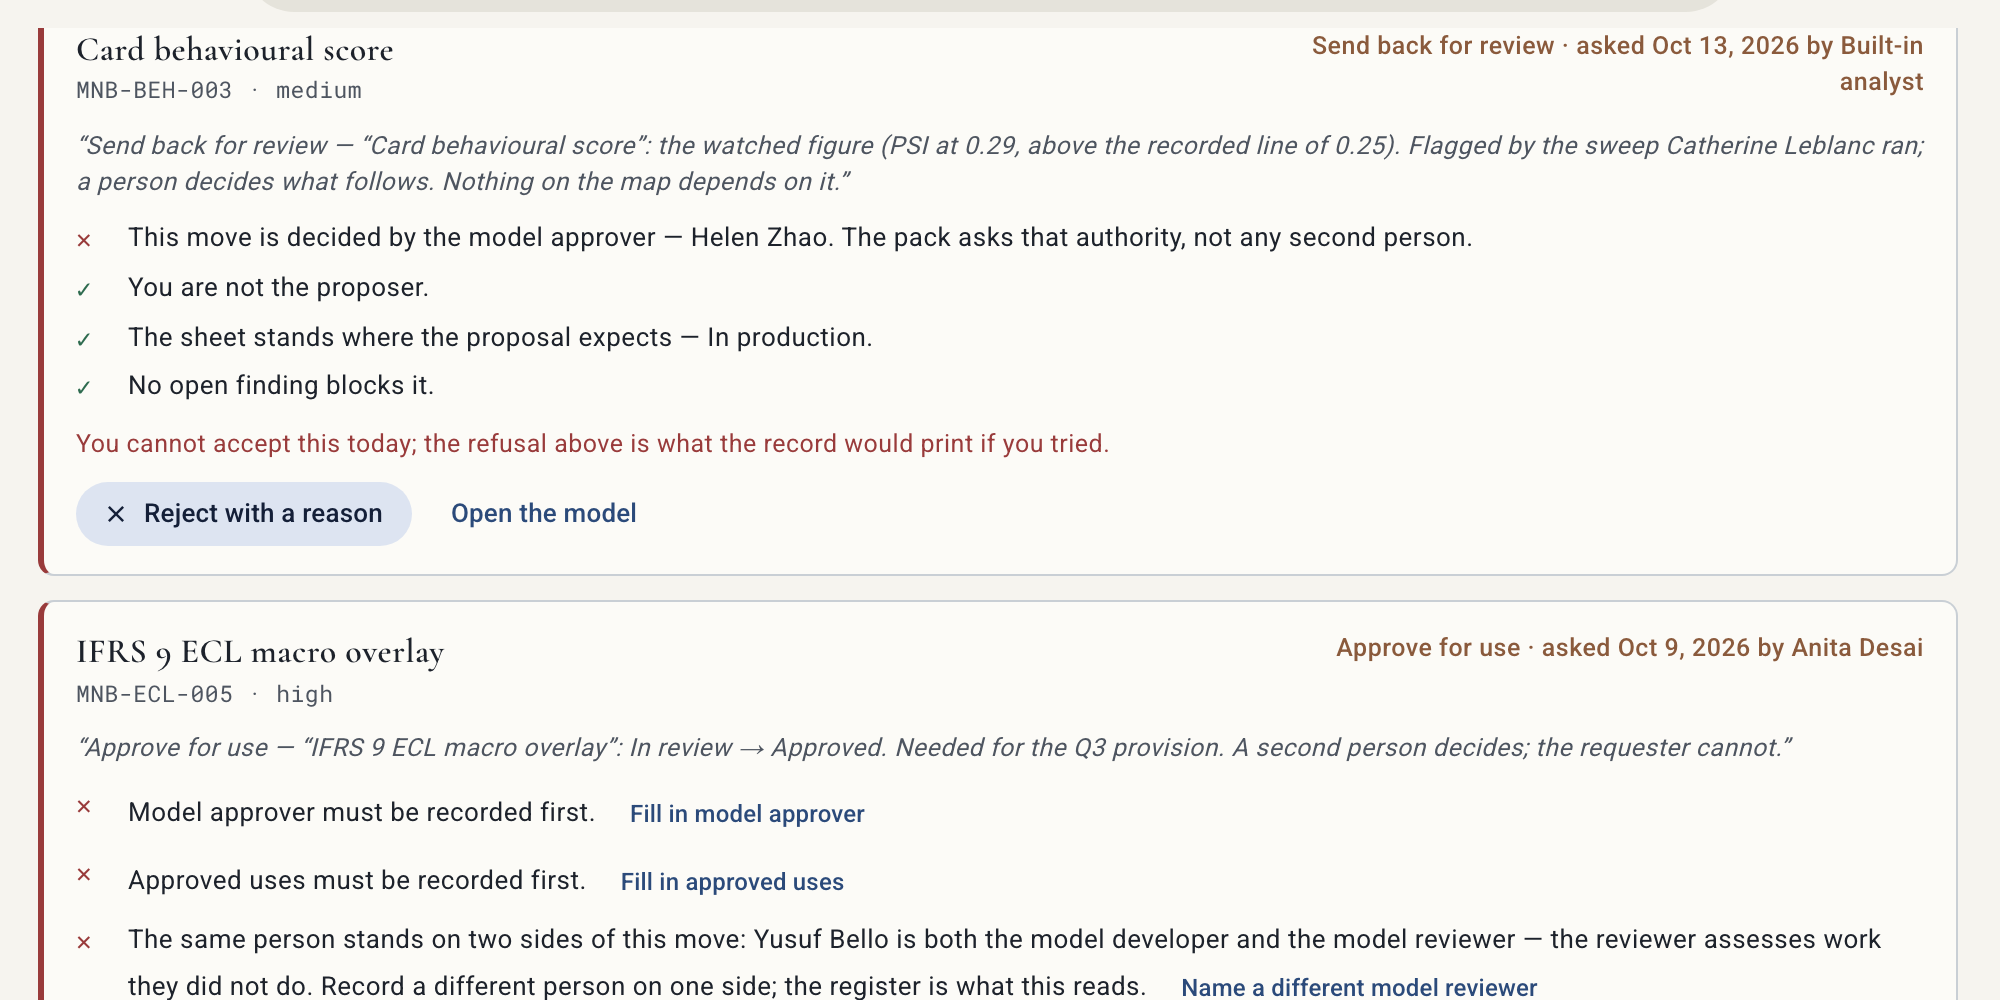
When a monitored metric crosses its threshold, the system proposes a return to review and a named person decides.
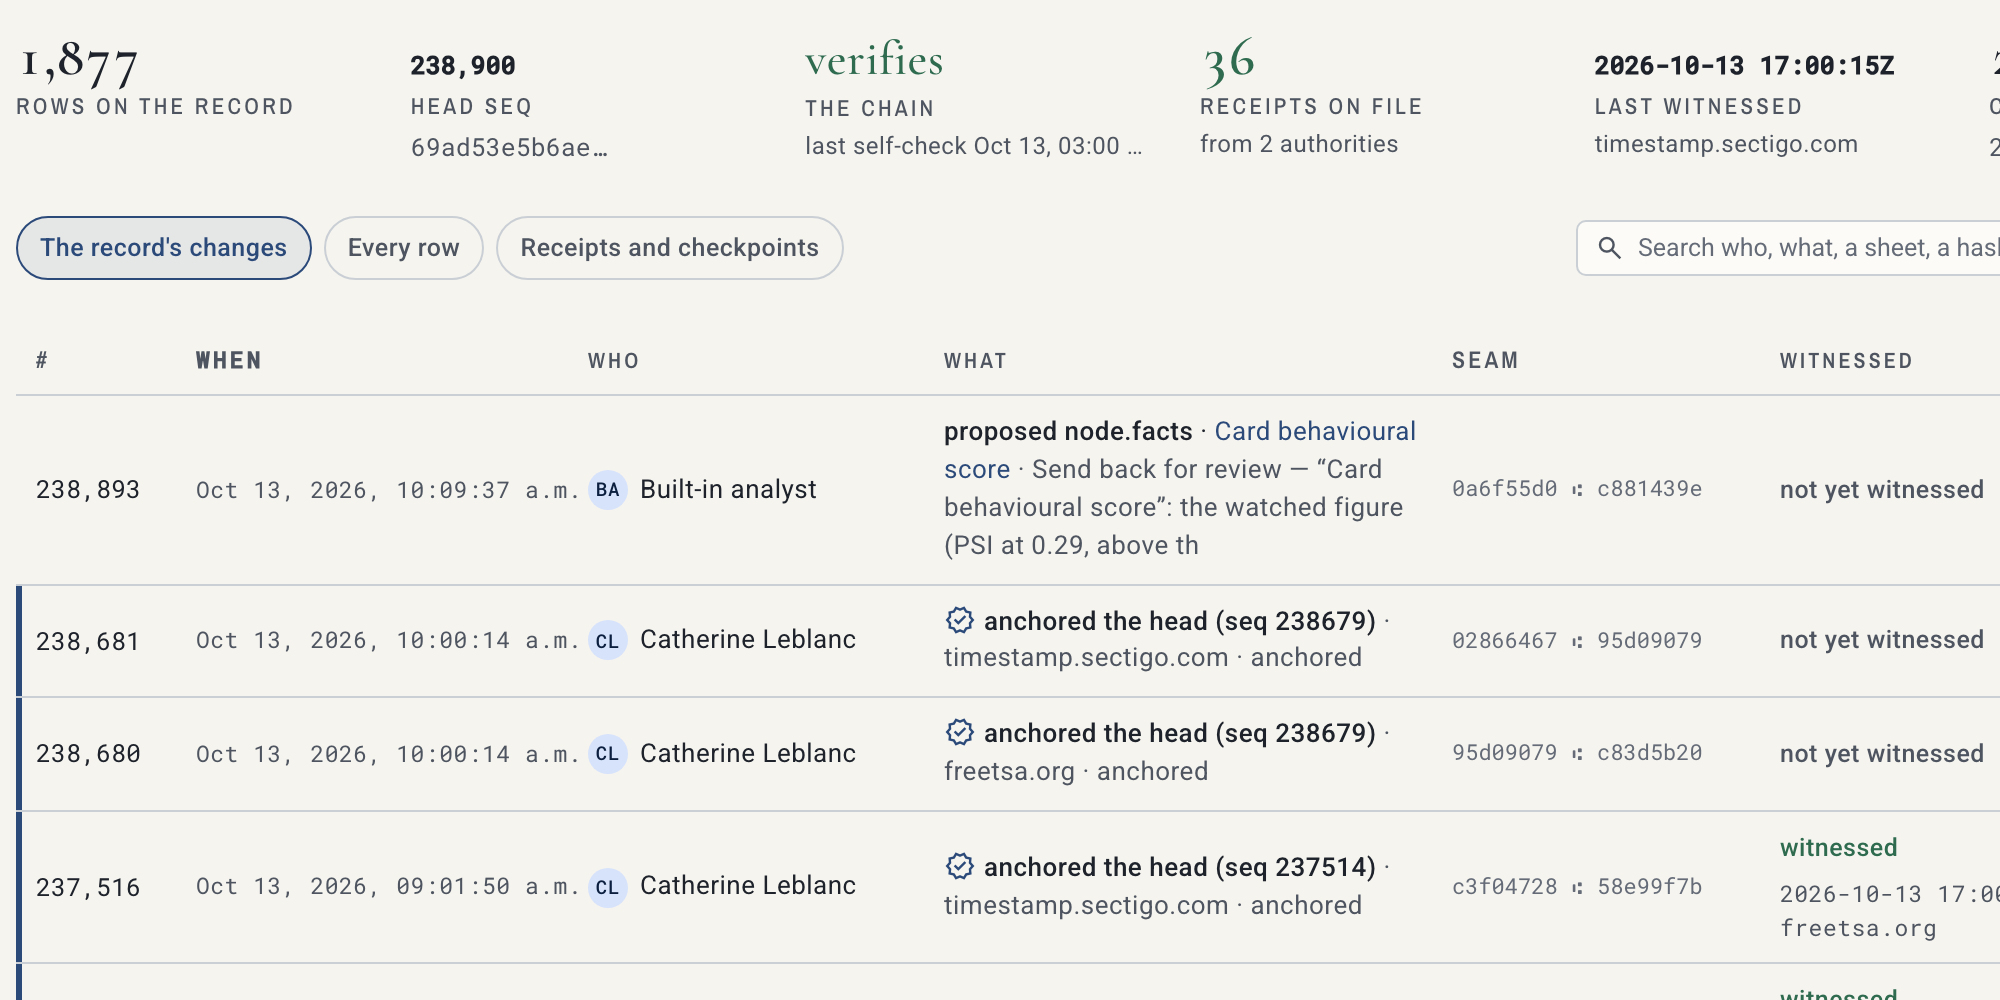
Every change is attributed, hash-chained to the previous one and time-stamped by independent authorities.
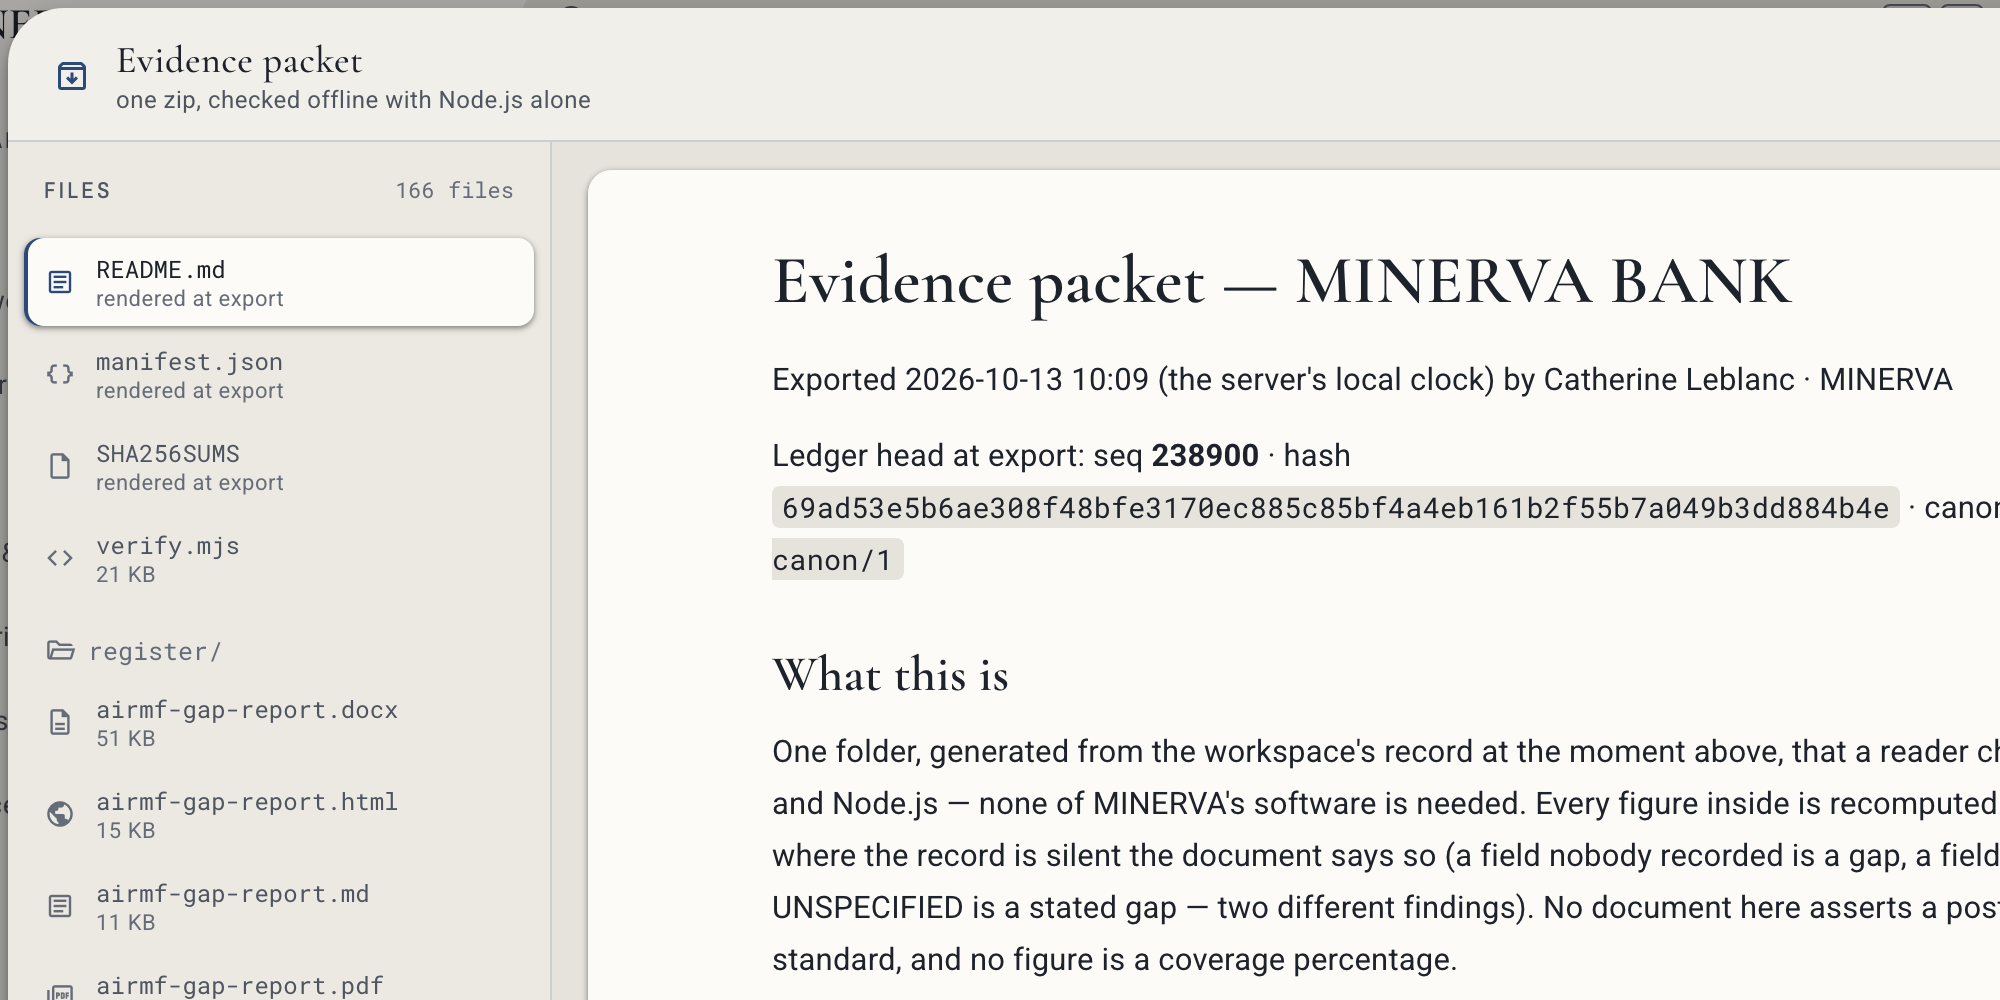
Every record, receipt and signed checkpoint in one file, which your examiner verifies offline without access to our systems.
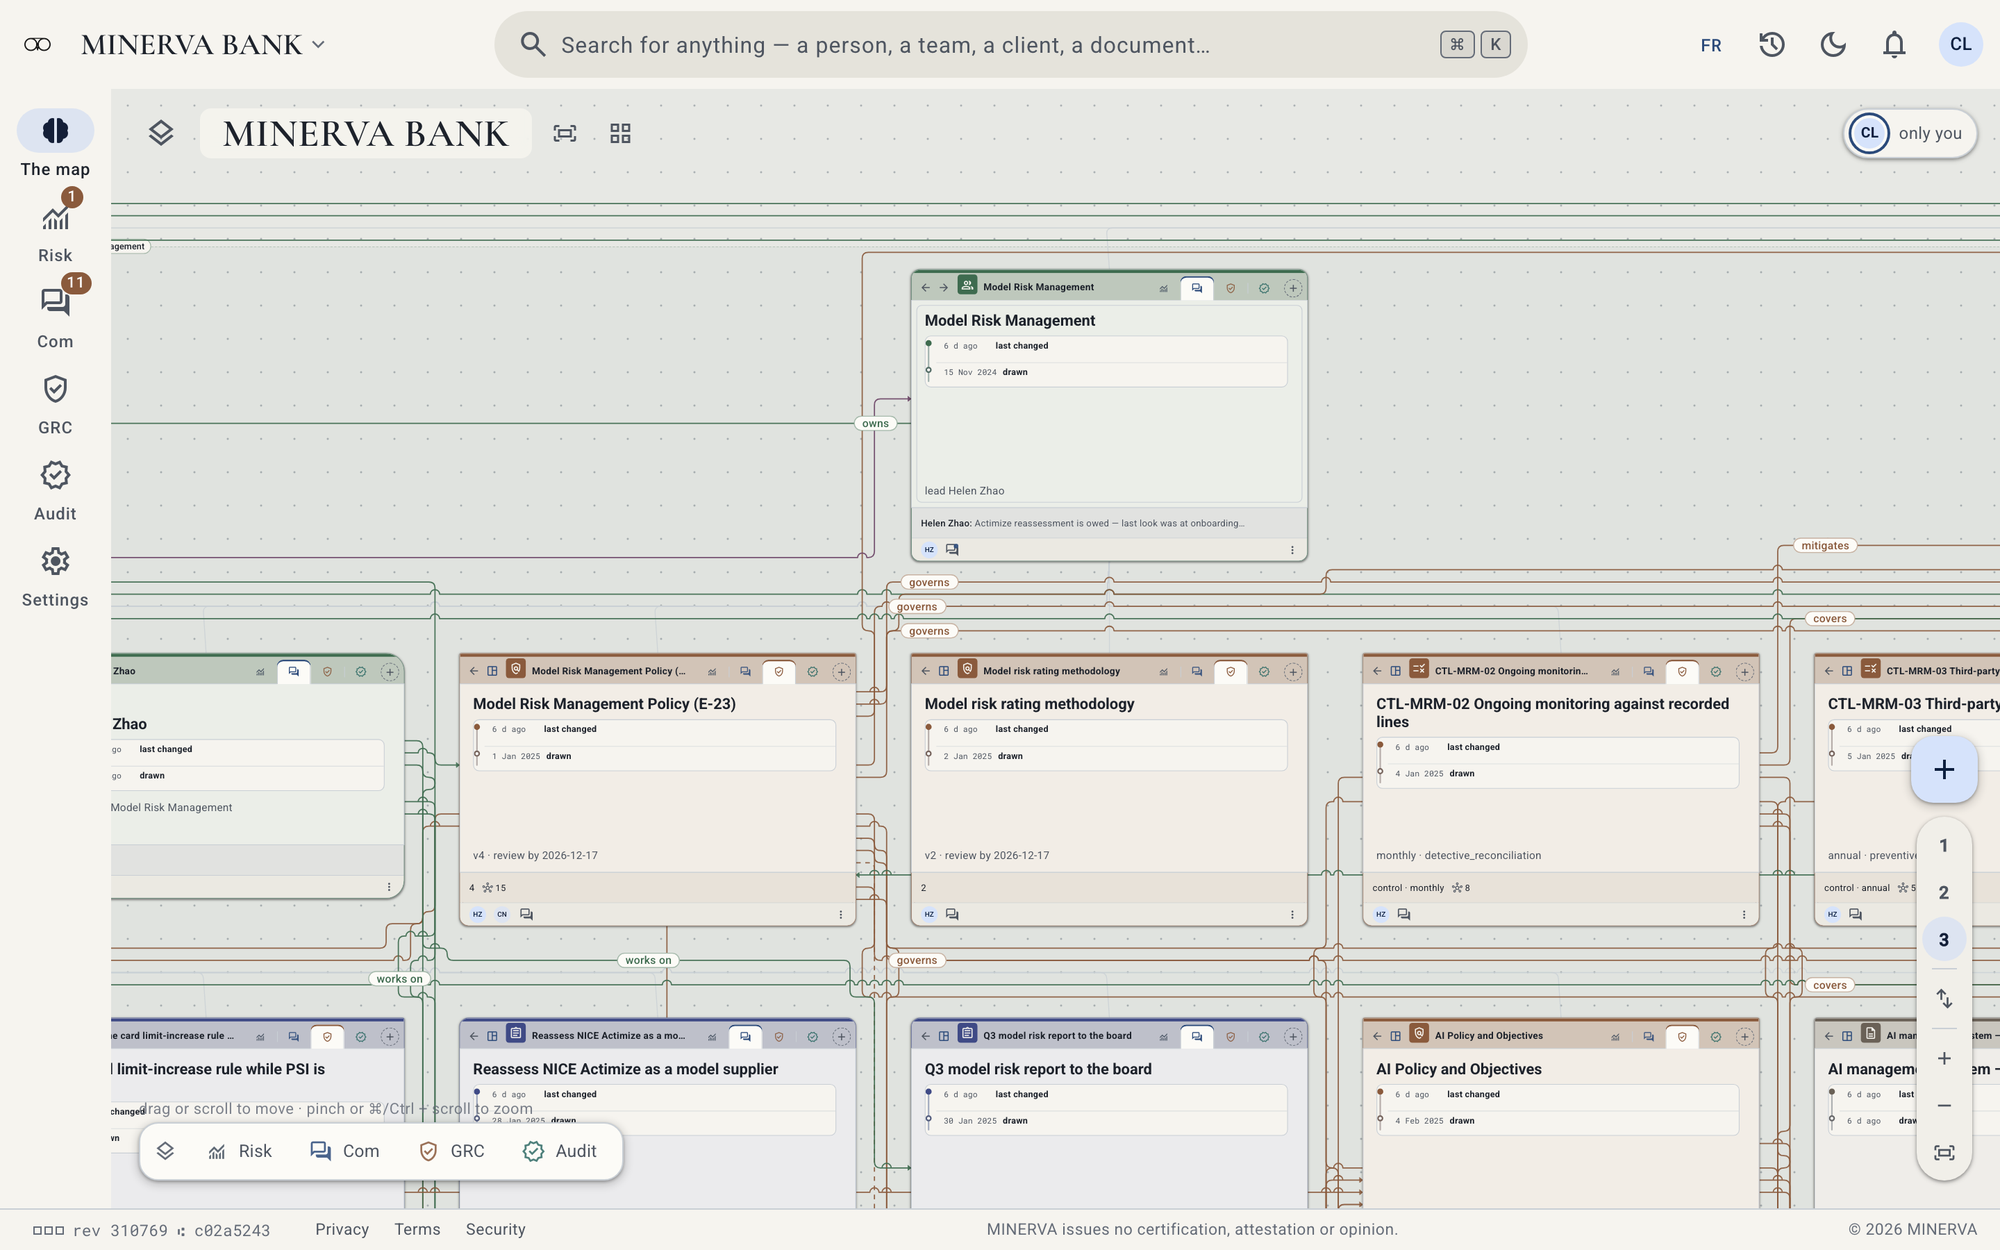
Your model risk function on one map: teams, the E‑23 policy, the rating methodology, controls and how they connect.
Guides In plain language